Sources reviewed 18 October 2026. Documentation-based guide; no physical-device test is claimed.
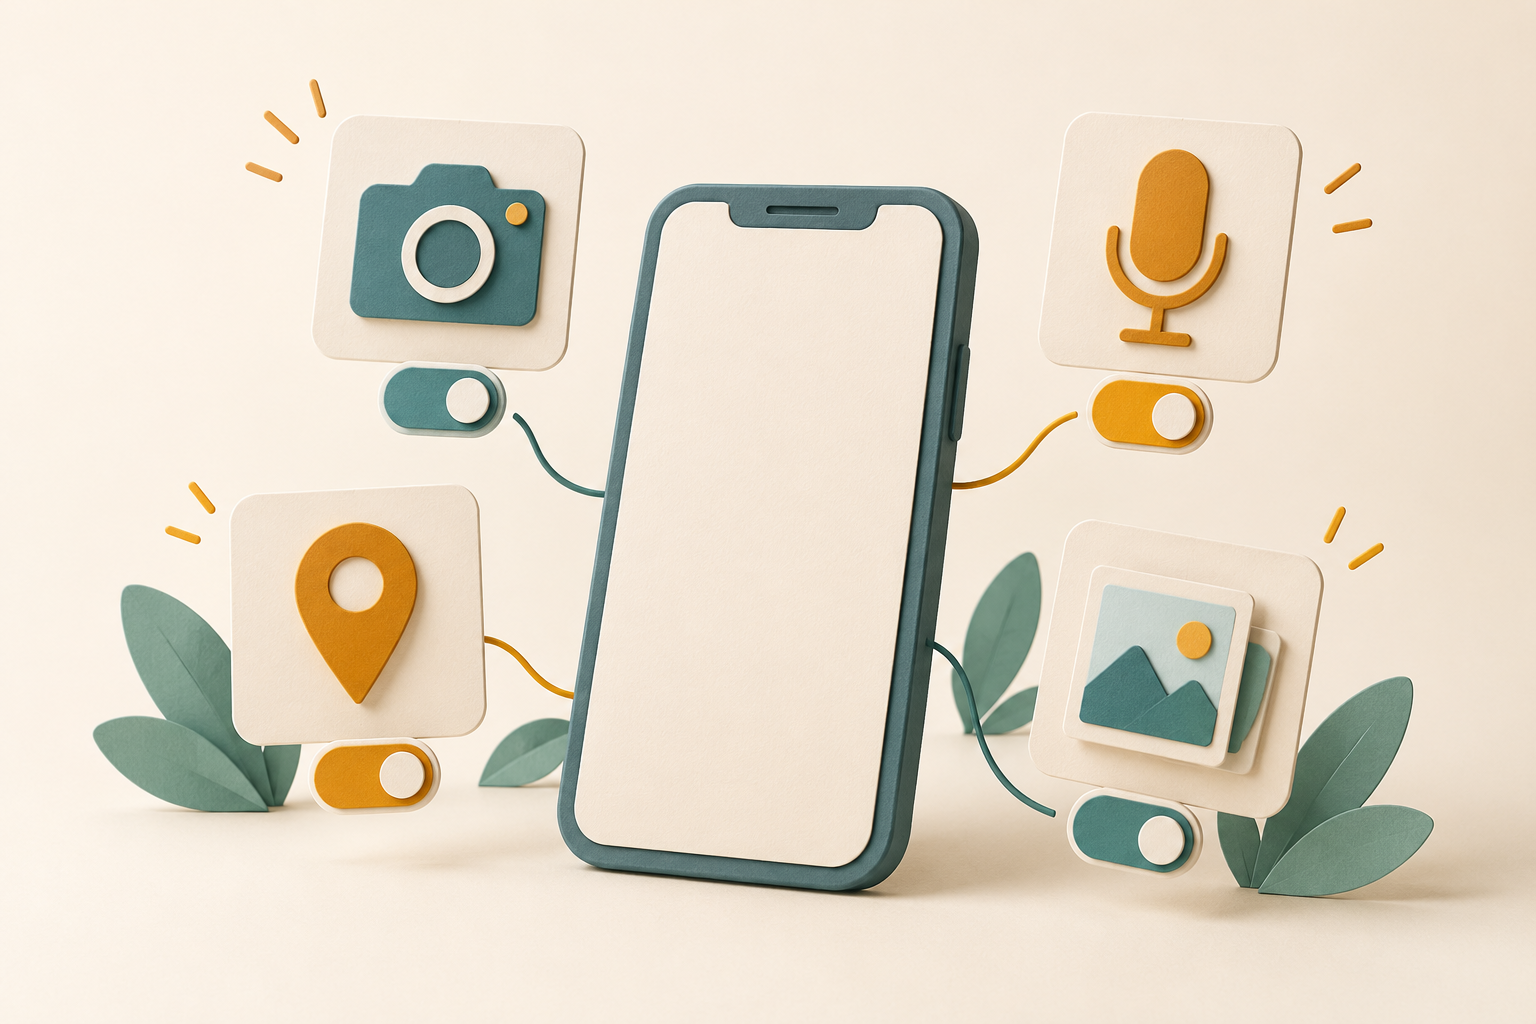
An Android permission lets an app use a particular protected capability or category of data. Review the requested access in relation to the feature you are using. Granting every permission is not a universal fix for an app problem.
Review one app’s access
Google’s permission management instructions use Settings → Apps → the app → Permissions. Choose the permission to review the available access options. Menus vary by device and Android release; some documented Pixel steps require Android 11 or later.
For supported permissions, choices may include access while using the app, asking each time or denying access. Location may additionally offer background access. Read the actual prompt: the same choices do not appear for every permission.
Match the request to a specific task
| Capability | A question worth asking |
|---|---|
| Camera | Am I taking a photo or joining video, or merely reading a document? |
| Microphone | Did I start a recording or call? |
| Location | Does the task need my current position, and at what precision? |
| Photos and videos | Which media am I trying to attach or edit? |
| Notifications | Do I want this app to send alerts? |
These are decision prompts, not claims that a particular app requests all of these permissions. A feature may explain why access is relevant, but it does not establish the trustworthiness of the publisher or the downloaded package.
When a feature stops working after you denied access
- Reproduce one specific task, such as joining audio or attaching a photo.
- Note the exact message instead of changing several settings at once.
- Review that app’s corresponding permission.
- Choose the narrowest available option that meets your intended use.
- Try the task again and record whether it changed.
For camera and microphone problems, Android also has device-wide privacy controls on supported versions. Review those separately when the individual permission appears correct. Do not assume a failed feature always requires reinstalling the app.
For a specific location example, see Google Maps location permissions, precision and Location Accuracy. It separates the app’s access choice from the phone’s location settings so you can investigate the control relevant to your task.
Review all apps using the same capability
Google also documents Permission manager, where you can inspect access by permission type. This is useful when your question is “which apps can access my microphone?” rather than “what can this one app access?” Review unfamiliar entries before granting anything new.
Check the privacy policy as well as permissions
Permissions describe access you can control; they do not provide a complete account of collection, storage or sharing. Before uploading a private document or connecting an account, compare the task you intend to perform with the publisher’s explanation of how it handles that information.
Google’s Data safety guide explains where to find the developer’s disclosures on a Play listing: open the app page, find Data safety and open See details. Those disclosures concern the Play-distributed app. Do not assume they describe a modified package from another website.
- Identify the publisher. Follow the privacy-policy link from the genuine listing or official website. Check that the policy names the app or service you are evaluating.
- List the information your task involves. For scanning, that might include the document image and extracted text. For account sync, it might include the information you enter and upload. These are questions to investigate, not assertions that every app collects them.
- Look for the purpose and destination. Distinguish processing on the phone from an upload to the publisher or another service. Check whether optional cloud or AI features have their own explanation.
- Check retention and deletion. Find the account/data-deletion route and any stated retention exceptions. Removing an Android permission or uninstalling the app should not be treated as confirmation that server-held information has been deleted.
- Keep a usable contact route. If the policy does not explain an important point, ask the publisher before submitting that information. You can choose a less sensitive sample or postpone the task.
Does “no data shared” mean nothing leaves the phone?
No. Google’s definitions include exceptions, such as some transfers to service providers and user-initiated sharing. The summary also covers multiple Play versions; practices can vary with use, region and age. Read the detailed policy rather than interpreting one label as a universal promise.
Who supplies the disclosure?
The developer does. Google’s Data safety requirements put responsibility for accuracy on the developer, including relevant third-party code. Treat a disclosure as evidence to compare with the app’s purpose and your observations, not as an independent audit of every action.
Privacy-policy section reviewed 23 October 2026 against the official sources linked above. No traffic inspection or device test is claimed.
Is a permission list a safety guarantee?
No. Permission review is one part of evaluating an app. Confirm its source and purpose too. Use our APK source and permission checklist, and distinguish access settings from update signature conflicts.
Should a download guide tell me to allow everything?
It should explain the permission needed for the task and its consequences. If a tutorial requests unrelated access without an explanation, pause and consult the publisher’s documentation. Browse the guide directory for task-specific help.