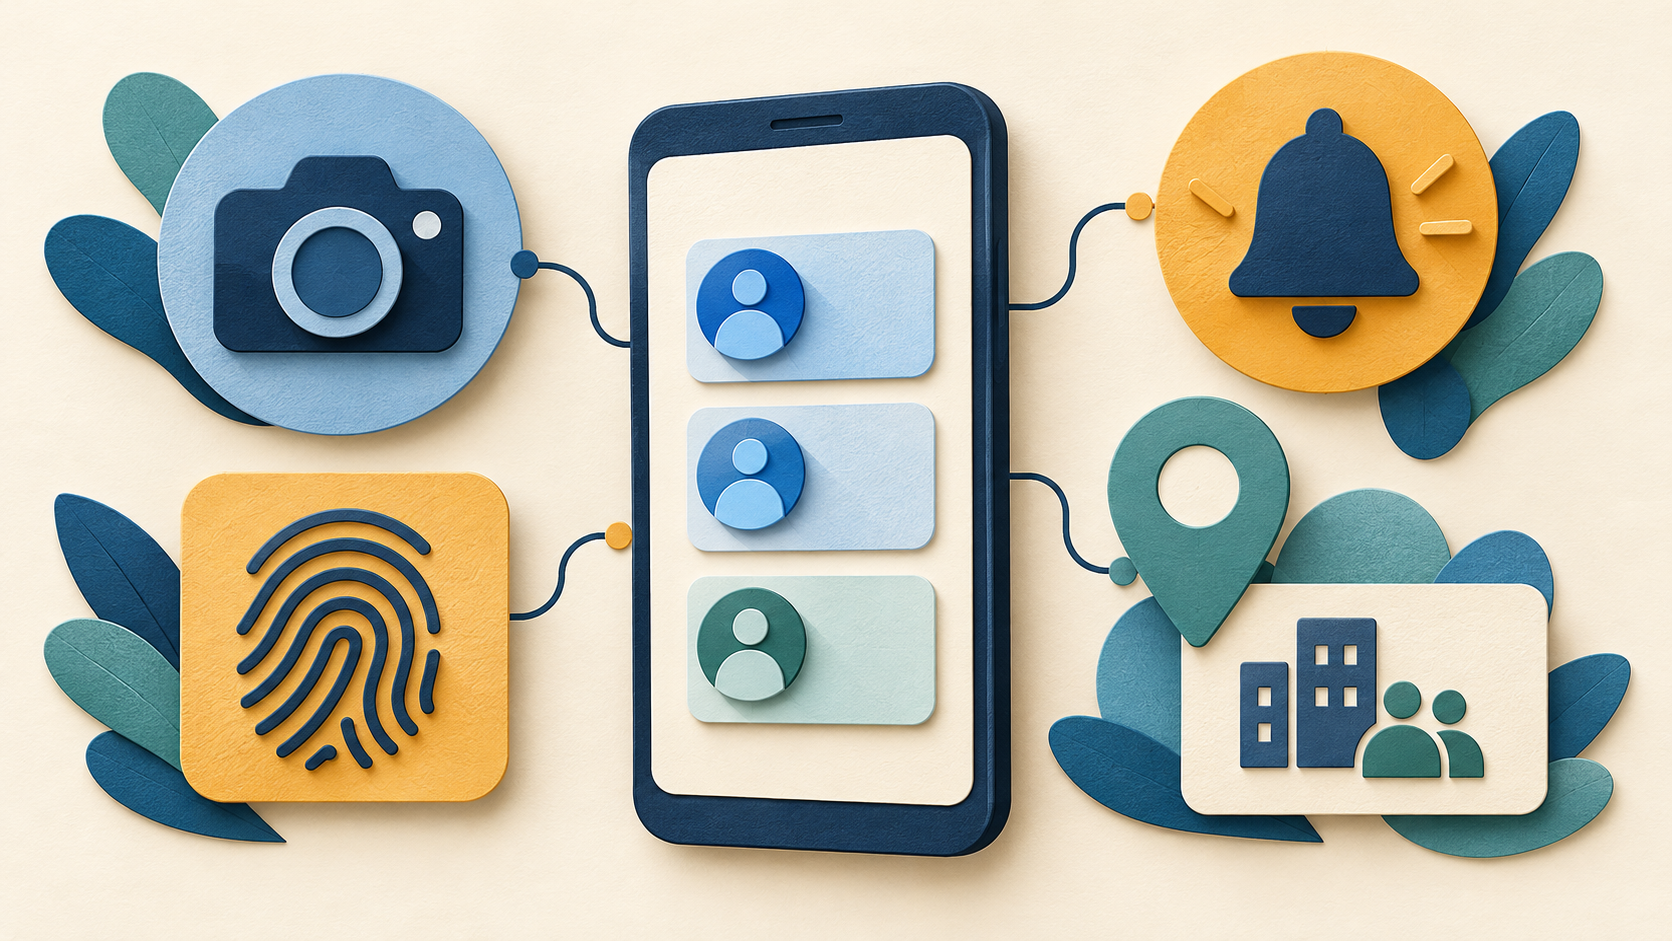
Microsoft Authenticator access requests should be assessed against the feature you are setting up. Camera access can support QR-code enrollment; notifications support eligible sign-in prompts; location access can be required by an organization’s access policy. These are different controls, and this guide does not advise approving every request or changing your account’s authentication methods indiscriminately.
Official documentation reviewed 20 October 2026. No installed-app permission manifest, account enrollment or sign-in was tested for this article. Android versions and work profiles can show different settings.
Match the request to the task
| Request or setting | Documented context | Question before proceeding |
|---|---|---|
| Camera | Scanning a setup QR code | Did you initiate enrollment on the genuine account’s security page? |
| Notifications | Sign-in prompts for eligible accounts | Does this account support that method, and did you initiate the sign-in? |
| Location | Organization policy for protected resources | Can your administrator explain the requirement? |
| App Lock | PIN or biometric access within the app | Are you changing an app-protection setting rather than granting a device resource? |
Camera access during QR setup
Microsoft’s account-addition guide explains that first-time setup can request Android camera access to scan a QR code. That request has a specific enrollment purpose; it is not evidence that every account operation needs the camera.
Start setup from the service’s genuine account-security page and read the instructions for the exact account type. A QR code used to enroll an authenticator can contain sensitive setup information. Do not post it in a public support thread, include it in a blog screenshot, or send it to someone who says they need it to “verify” your account.
If you did not begin enrollment, stop and establish what triggered the prompt. Do not add an account merely because a random page or message asks you to scan a code.
Notifications and missing approval prompts
Microsoft’s Authenticator troubleshooting guide lists notification settings and Android work/school prerequisites, including enabled Google Play services and Play Store. Check the relevant prerequisites and the app’s actual notification setting instead of treating every missing prompt as a camera-permission problem.
Identify whether the missing item is a push approval or a verification code you read from the app. They are different sign-in mechanisms. Check which device and account received the request, and do not approve an unexpected request to make a notification disappear.
For a managed account, your administrator can confirm the permitted method. Avoid removing a working authenticator registration while account access and alternative verification are uncertain.
Why location may be requested
Microsoft’s Authenticator FAQ describes GPS requests under an IT administrator’s resource-access policy, rather than a universal requirement for personal verification codes.
Confirm the resource, consequences and supported alternatives with your administrator. This article provides no policy bypass.
App Lock and old autofill tutorials
The FAQ describes App Lock as PIN or biometric protection, separate from device-resource permissions. Do not disable it as a generic fix.
Microsoft states that Authenticator autofill ended in mid-August 2025. Old autofill setup instructions should not be treated as a currently supported workflow.
Inspect the actual Android settings
Google’s app-permission instructions describe Settings > Apps > the app > Permissions. Review the permissions actually shown for your installation. A work profile can have separate management and device settings, so check that you are inspecting the intended instance of the app.
Do not substitute a permission list copied from another Microsoft product or another phone. Record the exact prompt, app version and action that triggered it. If a setting is managed, ask the organization rather than weakening unrelated protections.
When the expected sign-in request does not arrive
Start only with a sign-in you initiated, and distinguish a push request from a code displayed inside the app. Notification permission does not authorize an unexpected sign-in. Do not approve a different request merely because it appeared while you were troubleshooting.
- Identify the account and the verification method the genuine sign-in page actually requests. Keep the exact message and stage.
- Open Authenticator and check that the intended account is listed and the app is responsive. Unlock the app if required.
- Review the app’s notification setting and the phone’s silent/Do Not Disturb behavior. A hidden alert and an absent request are different observations.
- Check network connectivity, the supported app update and the device’s date/time. Microsoft’s authentication-incomplete explanation discusses these possible causes; none establishes a universal diagnosis.
- If the genuine sign-in page offers another verification method you previously configured, use only a method available for your account. For work or school, contact the administrator when the registered method or device is uncertain.
Could a request be going to an old phone?
Microsoft’s FAQ discusses this during credential registration when Authenticator remains active on another device. Check that documented scenario if it matches. Do not remove a working registration or erase the old phone until the replacement access and recovery route are established.
Should I remove the account and add it again immediately?
Preserve access first. Re-enrollment can require a working alternative verification route or administrator help. A missing prompt alone is not a reason to delete the account’s only usable registration. Use the publisher’s account-specific support process instead of changing unrelated protections.
Describe the account type, device/app versions and whether requests fail for one or all accounts when asking support. Keep one-time codes, QR enrollment secrets and recovery details private.
Missing-request section reviewed 23 October 2026. Documentation-based guidance; no account sign-in or enrollment test is claimed.
Frequently asked questions
Does refusing camera access delete my existing codes?
This guide does not claim that a camera toggle deletes registrations. Its documented role here is scanning during setup. Do not remove accounts or app data to troubleshoot the camera.
Should I approve a sign-in notification I did not initiate?
No. Check the account’s official security guidance and investigate the request. Permission to display notifications is not permission to authorize an unknown sign-in.
Does every account need continuous location access?
No such general requirement is established here. Check the specific organization policy and feature requesting it.
What information can I safely send to support?
Describe the device, Android and app version, account type and redacted error. Never send passwords, one-time codes, QR enrollment secrets or recovery codes.
For general access controls, read our Android permissions guide. The Proton Pass autofill guide covers a different product and should not be treated as Authenticator setup instructions. Browse our Android guide directory for related help.